Client: Eight companies of Financial Group A (financial enterprises)
Project Duration
– Seven financial affiliates — carried out over six months in 2011; ISO27001 and BS10012 certifications obtained
– One additional financial affiliate — carried out over 2.5 months in 2012; ISO27001 and BS10012 certifications obtained
Project Background and Subject
In line with the financial group’s policy of achieving a global level of information security and personal information protection, eight affiliates commissioned consulting to obtain ISO27001, the international standard for information security, and BS10012, the BSI standard for personal information. The first seven financial affiliates pursued the two certification consulting engagements sequentially and at the same time, and obtained the certifications. In the second half of the year, the remaining company secured a budget, received consulting for both certifications, and obtained the certifications.
At the time the project was carried out, major financial institutions had suffered large-scale personal information leakage incidents, and as the Personal Information Protection Act and its Enforcement Decree were passed, the business climate aligned in a timely way, so the clients’ working-level staff had little difficulty driving the engagement. Because ISO27001 and BS10012 share some control items, pursuing the two certifications at the same time brought efficiency in cost and time from the client’s perspective. By securing an operational management system aligned with the certification specifications, efficiency could also be gained in change management among related internal organizations. Most companies and institutions struggle to maintain certification after it is obtained, because they are unfamiliar, internally and externally, with that environment. One round of surveillance-audit support was therefore provided so that they could settle into the changed operational management environment. The certification scope was the same in every case: certification consulting covered the entire IT organization, and every affiliate obtained certification as planned.
IT and Information Security Environment
Business and IT Environment
The client’s main business areas differed, covering investment, life insurance, capital, and regional banking.
The IT environment was not large in scale, and the volume of personal information that had to be protected varied greatly depending on the organization and the work being processed.
Information Protection Environment
Most affiliates were financial companies regulated by the Financial Supervisory Service, but because they were smaller second-tier or third-tier financial companies, their environment was considerably weaker than that of first-tier financial companies in terms of security organization and policy. The security solutions they held were basic network-domain solutions such as firewalls and IPS, and they provided external services related to electronic finance. Belonging to an industry with a very high dependence on IT, the client divided and operated security activities by domain under a CSO, and by operating an information protection committee and a working-level council it maintained an organizational system able to prevent and respond in advance to enterprise-wide information protection issues.
Project CSF
- Accurately explain the control items to stakeholders within the ISO27001 and BS10012 certification scope and build consensus
- Accurately identify information assets inside and outside the certification scope (in particular, information assets in non-IT areas such as documents)
- Build understanding of R&R and consensus among stakeholders for maintaining the certification after it is obtained
- Establish and revise policies and guidelines suited to each affiliate’s environment and conditions
Key Activities and Deliverables
| Execution Phase | Key Work Performed | Resulting Deliverables |
|---|---|---|
| Certification Scope Definition | – Analysis of the IT and information protection status – Consultation on and confirmation of the certification scope | – ISO27001 certification scope definition – BS10012 certification scope definition |
| Information Asset Assessment and Vulnerability Analysis | – Classification of information assets and criticality assessment – Vulnerability assessment of information assets – Internal and external penetration testing | – Asset inventory and criticality results – Server vulnerability assessment report – Network and security system vulnerability assessment results report – PC and DBMS vulnerability assessment report – Penetration test report |
| Management System Status Analysis and Risk Assessment | – Vulnerability assessment by ISO27001 certification control – Vulnerability assessment by BS10012 certification control – Review of related documents, interviews, and on-site inspection – Risk assessment and establishment of a treatment plan | – ISO27001 management system gap analysis – BS10012 management system gap analysis – Risk assessment report – Risk treatment plan |
| Establishment of the Certification Management System | – Establishment and revision of information security policies and guidelines – Establishment of an information protection improvement plan – Information protection effectiveness measurement table – Preparation of requirement documents by control item – Analysis of information protection effectiveness | – Information security policy and guidelines – Information security master plan report – Management system Statement of Applicability (SOA) report – Effectiveness measurement indicator report |
| Support for Implementing the Certification System | – Support for securing implementation evidence by control item – Conduct of the internal audit and improvement | – Support for implementation evidence of guidelines and procedures – Internal audit plan and report |
| Certification-Related Support | – Training conducted in preparation for the audit – Support for responding to the certification audit and the document review – Support for responding to nonconformities | – Pre-audit training plan and training materials – Nonconformity corrective action plan |
Characteristics of the Consulting Engagement
Because most affiliates had a weak information security environment, they were partial or considerably inadequate in the information security and personal information protection policies required by the certification specifications. Related guidelines and manuals were used as issued by the higher supervisory authority, or documents from similar affiliates were operated without being updated, and work was carried out without standardized criteria according to each staff member’s individual competence.
In particular, information assets within the certification scope had not been organized, so confirming the information asset inventory took the most time. During the criticality assessment, there was difficulty in helping owners and custodians understand the assessment process and in deriving the assessment results. Because the management system was relatively inadequate, there was no great difficulty in designing the information security and personal information protection management systems and explaining them to the people concerned.
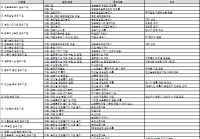
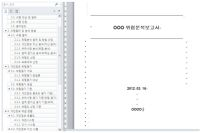
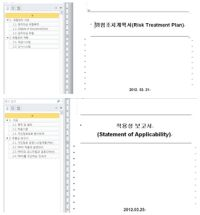
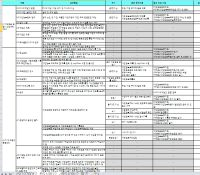
- Example deliverables: gap analysis by control item, risk analysis report, risk treatment plan, statement of applicability, management system operation plan, and list of evidence by domain