
VPN Overview
A VPN (Virtual Private Network) is a network service that builds a private network over a public network so that a user can use it as if it were that user’s own private premises network or leased line.
- Types of VPN
1. Site to Site
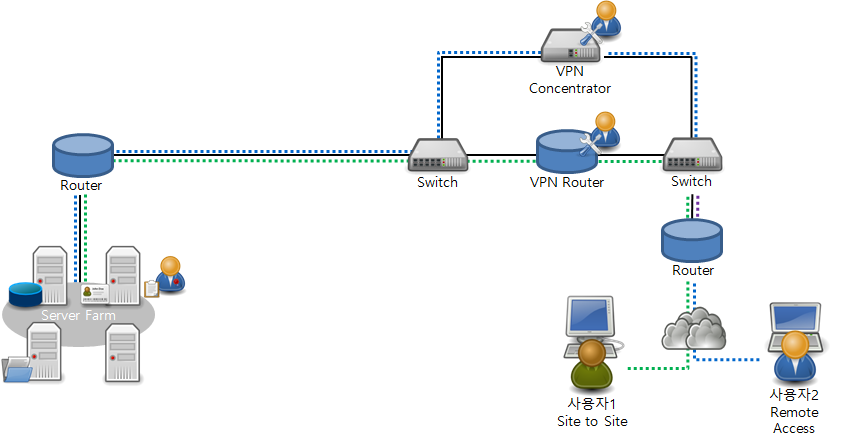
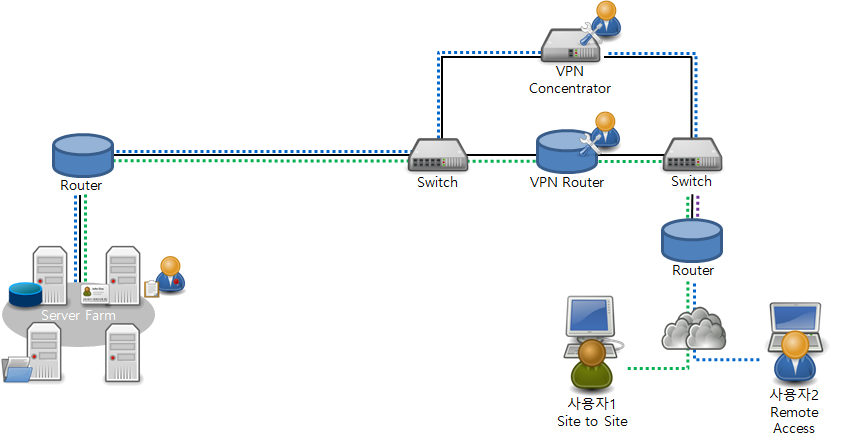
In the figure below, “User 1” is connected to the headquarters network from an external site (branch), generally through a VPN router.
2. Remote Access
“User 2” is a business traveler, a home-based worker, or a similar user who connects to the headquarters network through a VPN concentrator.
- VPN Security Threats
1. Network Topology Discovery: The network structure is exposed, and a malicious user can use it as key information for identifying an entry point for hacking.
2. Password attack: If a weak password is used during VPN login, it can be exposed to a rainbow table or a brute-force attack.
3. Unauthorized access: An attack can be carried out through a bypass path.
4. Man-in-the-middle attack: An intermediary (an attacker) can eavesdrop on information sent by authorized users, or alter that information and forward it.
5. Packet sniffing: Network traffic can be eavesdropped on and analyzed through a sniffer.
*Security threats such as those above should be addressed with the security architecture below.
VPN Security Architecture
| Site to Site VPN Security Guide | Mitigated Security Threat | |
|---|---|---|
| Appropriate configuration of the internet-edge router and the VPN router | -Primary filtering through the internet edge router: VPN traffic from outside is limited to specific IP addresses and protocols -Monitor access attempts against nearby equipment through an IDS/IPS -The VPN router between sites restricts communication to a specific destination IP (the VPN router) and applies control by setting restricted system IPs | Network Topology Discovery |
| Use of an OTP generator | -Strengthen password authentication by using a one-time password | Password Attack(Password Attack) |
| Appropriate configuration of the internal firewall | -Control decrypted packet traffic on unauthorized ports through the firewall | Unauthorized Access(Unauthorized Access) |
| Appropriate configuration of the VPN router | -Security of remote traffic through path encryption: path-encrypted communication between sites through the VPN routers | Man-in-the-Middle(Man-in-the-Middle Attack) |
| Switched Network structure | -Neutralize sniffing through a switched structure | Packet sniffers(Packet Sniffing) |
| Remote Access VPN Security Guide | Mitigated Security Threat | |
|---|---|---|
| Appropriate configuration of the internet-edge router | -Primary filtering through the internet edge router: VPN traffic from outside is limited to specific IP addresses and protocols -Monitor access attempts against nearby equipment through an IDS/IPS -Control access to the internal network through authentication by the VPN concentrator | Network Topology Discovery |
| Use of an OTP generator | -Strengthen security through OTP authentication: the user’s connection to the VPN concentrator is controlled through an access-control server in the server farm | Password Attack(Password Attack) |
| Appropriate configuration of the internal firewall | -Control decrypted packet traffic on unauthorized ports through the firewall | Unauthorized Access(Unauthorized Access) |
| Path encryption by the encryption module of the VPN concentrator | -Security of remote traffic through path encryption | Man-in-the-Middle(Man-in-the-Middle Attack) |
| Switched Network structure | -Neutralize sniffing through a switched structure | Packet sniffers(Packet Sniffing) |
- Security control modules related to each actor
| Actor | Security control items |
|---|---|
 Security monitoring | AC- Access Control Group(Access Control), AT- Awareness And Training Group(Awareness and Training), AU- Audit And Accountability Group(Audit and Accountability), \\CA- Certification, Accreditation And Security Assessments Group(Certification, Accreditation, and Security Assessments), CM- Configuration Management Group(Configuration Management), \\CP- Contingency Planning Group(Contingency Planning), IA- Identification and Authentication Group(Accounts and Privileges), \\IR- Incident Response Group(Incident Response), MA- Maintenance Group(Business Continuity), MP- Media Protection Group(Media Protection), \\PE- Physical and Environmental Protection Group(Physical Security), PL- Planning Group(Planning), PS- Personnel Security Group(Personnel Security), \\RA- Risk Assessment Group(Risk Assessment), SA- System and Services Acquisition Group(System and Services Acquisition), \\SC- System and Communication Protection Group(System and Communications Security), SI- System and Information Integrity Group(System and Information Integrity) |
 Equipment administrator | AC- Access Control Group(Access Control), AT- Awareness And Training Group(Awareness and Training), AU- Audit And Accountability Group(Audit and Accountability), \\CA- Certification, Accreditation And Security Assessments Group(Certification, Accreditation, and Security Assessments), CM- Configuration Management Group(Configuration Management), \\CP- Contingency Planning Group(Contingency Planning), IA- Identification and Authentication Group(Accounts and Privileges), \\IR- Incident Response Group(Incident Response), MA- Maintenance Group(Business Continuity), MP- Media Protection Group(Media Protection), \\PE- Physical and Environmental Protection Group(Physical Security), PL- Planning Group(Planning), PS- Personnel Security Group(Personnel Security), \\RA- Risk Assessment Group(Risk Assessment), SA- System and Services Acquisition Group(System and Services Acquisition), \\SC- System and Communication Protection Group(System and Communications Security), SI- System and Information Integrity Group(System and Information Integrity) |
 Equipment administrator | AC- Access Control Group(Access Control), AT- Awareness And Training Group(Awareness and Training), AU- Audit And Accountability Group(Audit and Accountability), \\CA- Certification, Accreditation And Security Assessments Group(Certification, Accreditation, and Security Assessments), CM- Configuration Management Group(Configuration Management), \\CP- Contingency Planning Group(Contingency Planning), IA- Identification and Authentication Group(Accounts and Privileges), \\IR- Incident Response Group(Incident Response), MA- Maintenance Group(Business Continuity), MP- Media Protection Group(Media Protection), \\PE- Physical and Environmental Protection Group(Physical Security), PL- Planning Group(Planning), PS- Personnel Security Group(Personnel Security), \\RA- Risk Assessment Group(Risk Assessment), SA- System and Services Acquisition Group(System and Services Acquisition), \\SC- System and Communication Protection Group(System and Communications Security), SI- System and Information Integrity Group(System and Information Integrity) |
 Equipment administrator | AC- Access Control Group(Access Control), AT- Awareness And Training Group(Awareness and Training), AU- Audit And Accountability Group(Audit and Accountability), \\CA- Certification, Accreditation And Security Assessments Group(Certification, Accreditation, and Security Assessments), CM- Configuration Management Group(Configuration Management), \\CP- Contingency Planning Group(Contingency Planning), IA- Identification and Authentication Group(Accounts and Privileges), \\IR- Incident Response Group(Incident Response), MA- Maintenance Group(Business Continuity), MP- Media Protection Group(Media Protection), \\PE- Physical and Environmental Protection Group(Physical Security), PL- Planning Group(Planning), PS- Personnel Security Group(Personnel Security), \\RA- Risk Assessment Group(Risk Assessment), SA- System and Services Acquisition Group(System and Services Acquisition), \\SC- System and Communication Protection Group(System and Communications Security), SI- System and Information Integrity Group(System and Information Integrity) |
 Account administrator | AC- Access Control Group(Access Control), AT- Awareness And Training Group(Awareness and Training), AU- Audit And Accountability Group(Audit and Accountability), \\CA- Certification, Accreditation And Security Assessments Group(Certification, Accreditation, and Security Assessments), CM- Configuration Management Group(Configuration Management), \\CP- Contingency Planning Group(Contingency Planning), IA- Identification and Authentication Group(Accounts and Privileges), \\IR- Incident Response Group(Incident Response), MA- Maintenance Group(Business Continuity), MP- Media Protection Group(Media Protection), \\PE- Physical and Environmental Protection Group(Physical Security), PL- Planning Group(Planning), PS- Personnel Security Group(Personnel Security), \\RA- Risk Assessment Group(Risk Assessment), SA- System and Services Acquisition Group(System and Services Acquisition), \\SC- System and Communication Protection Group(System and Communications Security), SI- System and Information Integrity Group(System and Information Integrity) |
 User | AC- Access Control Group(Access Control), AT- Awareness And Training Group(Awareness and Training), AU- Audit And Accountability Group(Audit and Accountability), \\CA- Certification, Accreditation And Security Assessments Group(Certification, Accreditation, and Security Assessments), CM- Configuration Management Group(Configuration Management), \\CP- Contingency Planning Group(Contingency Planning), IA- Identification and Authentication Group(Accounts and Privileges), \\IR- Incident Response Group(Incident Response), MA- Maintenance Group(Business Continuity), MP- Media Protection Group(Media Protection), \\PE- Physical and Environmental Protection Group(Physical Security), PL- Planning Group(Planning), PS- Personnel Security Group(Personnel Security), \\RA- Risk Assessment Group(Risk Assessment), SA- System and Services Acquisition Group(System and Services Acquisition), \\SC- System and Communication Protection Group(System and Communications Security), SI- System and Information Integrity Group(System and Information Integrity) |